Your medical practice needs analytics.
You need to know which pages attract patients, which campaigns generate appointments, where visitors abandon your website, and which services produce qualified inquiries.
But there is a dangerous assumption:
“If an analytics tool is widely used, it must be safe for healthcare websites.”
That assumption can create a serious HIPAA analytics problem.
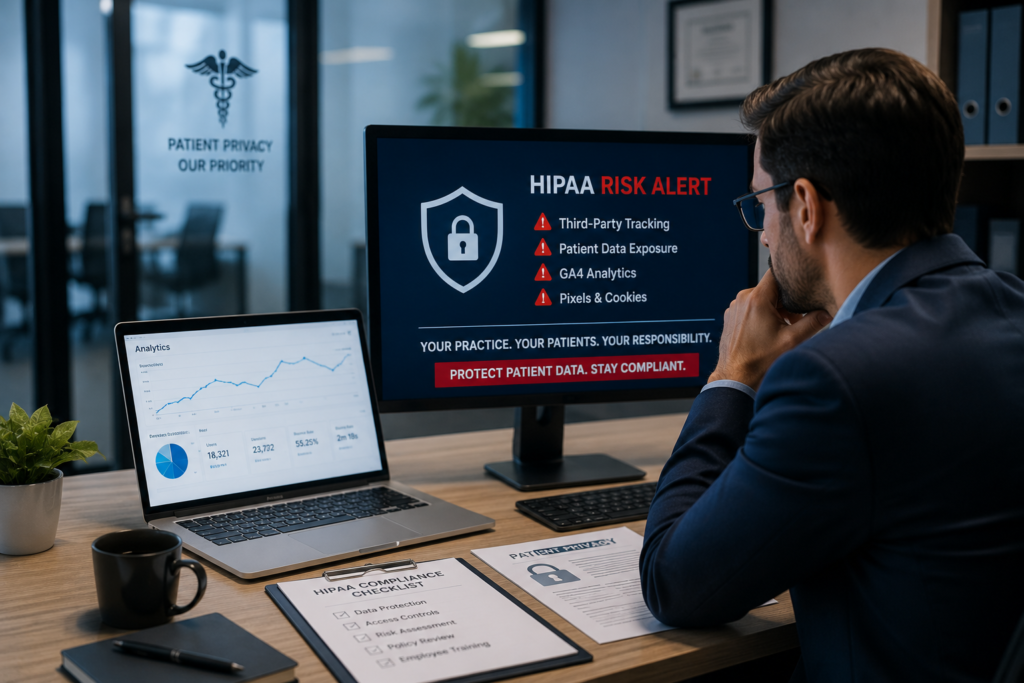
Google Analytics 4, Meta Pixel, Facebook Pixel, session-recording scripts, advertising tags, cookies, and other tracking technologies can collect information about how people interact with healthcare websites. Depending on the page, the information involved, and the surrounding circumstances, those technologies can create privacy and HIPAA Analytics concerns.
HHS specifically warns that tracking technologies used by HIPAA-regulated entities can disclose information to third parties, including identifiers, IP addresses, geographic information, appointment information, and information users enter or select on websites.
Google also states that HIPAA-regulated entities must not use Google Analytics in a way that exposes PHI to Google and says Google Analytics does not represent itself as HIPAA-compliant or offer a Business Associate Agreement for the service.
The real issue isn’t whether HIPAA Analytics are valuable.
It’s whether your practice is collecting marketing data at the expense of patient privacy.
What Is the HIPAA Analytics Trap?
The HIPAA Analytics Trap happens when a healthcare organization installs ordinary marketing analytics without evaluating what information those tools can receive from patient-facing pages.
A practice may install GA4 to measure:
- Organic traffic
- Landing-page performance
- Appointment-button clicks
- Form interactions
- Campaign performance
- Conversion rates
- User journeys
Then a marketer adds:
- Meta Pixel
- Google Ads tags
- LinkedIn Insight Tag
- TikTok Pixel
- Call-tracking scripts
- Session-recording software
- Heatmaps
- Retargeting scripts
Each tool may appear harmless by itself.
The risk emerges from the data flow.
HHS defines online tracking technologies broadly enough to include cookies, web beacons, tracking pixels, session-replay scripts, and fingerprinting scripts. Its guidance explains that third-party technologies can transmit information directly to the technology vendor.
For a healthcare organization, the question should therefore be:
What information does this script receive when a patient visits this particular page?
That question is more important than simply asking:
“Does our website have Google Analytics installed?”
Why GA4 HIPAA Compliance Is More Complicated Than a Tracking Code
The phrase GA4 HIPAA compliance can create a misleading impression that there is a simple configuration switch.
There isn’t.
Google’s own guidance says HIPAA-regulated customers must avoid using Google Analytics in ways that create obligations under HIPAA for Google and must not expose PHI to Google. Google also says it does not make representations that Google Analytics satisfies HIPAA requirements and does not provide a BAA for Google Analytics.
That distinction matters.
A practice could have:
GA4 + a privacy policy + cookie banner
and still have a problem if PHI is transmitted to a third party.
For example, consider a patient visiting a page specifically related to a particular medical condition.
If tracking technology can associate that visit with identifying information or other data that makes the individual identifiable, the privacy analysis becomes much more complicated.
HHS specifically notes that even visits to unauthenticated webpages can potentially involve PHI depending on the circumstances.
So Google Analytics HIPAA questions cannot be answered by looking only at whether a visitor logged into a patient portal.
The page’s purpose, information collected, identifiers, and disclosures all matter.
Why Healthcare Tracking Pixels Deserve a Separate Audit
A healthcare tracking pixel is usually a small piece of code that sends information about user activity to another platform.
Examples include:
- Meta Pixel
- Facebook Pixel
- Advertising pixels
- Conversion pixels
- Retargeting tags
- Social media tracking scripts
HHS specifically identifies technologies such as the Meta/Facebook Pixel and Google Analytics as examples of tracking technologies that have raised privacy and security concerns in healthcare.
The problem is not simply that a pixel exists.
The problem is what the pixel can observe and transmit.
Imagine a healthcare website with these pages:
/depression-treatment/
/fertility-treatment/
/substance-use-treatment/
/cancer-treatment/
/sexual-health/
A generic advertising strategy might treat every page like an ordinary commercial landing page.
Healthcare privacy requires a more careful assessment.
The URL, page context, event name, form interaction, identifier, or other information associated with the visitor may create additional risk depending on the circumstances.
That’s why HIPAA Analytics tracking pixels deserve a dedicated technical review rather than being added automatically through Google Tag Manager.
Meta Pixel HIPAA Risk Can Start With a Marketing Goal
The typical marketing objective is straightforward:
“Track which visitors become leads.”
The implementation may include:
PageView → Lead → Appointment → Conversion
That sounds reasonable for an e-commerce company.
Healthcare is different.
If a patient interacts with a medical service page and the tracking system sends information to an advertising platform, the practice needs to evaluate whether that disclosure is permissible.
HHS’s tracking-technology guidance specifically addresses information transmitted through tracking technologies and explains that HIPAA Analytics obligations can apply when regulated entities disclose PHI to tracking technology vendors.
This makes Meta Pixel HIPAA risk a technical and compliance question not merely a Facebook advertising question.
A practice should not assume that removing a person’s name from an event automatically removes all privacy concerns.
The Biggest Mistake: Treating the Website as “Public,” Therefore Safe
A common argument is:
“The website is public, so HIPAA doesn’t apply.”
That is too simplistic.
HHS distinguishes between authenticated and unauthenticated webpages and explains that information collected through tracking technologies can still involve PHI on unauthenticated pages depending on the circumstances.
For example, a public page about a medical condition may reveal sensitive information when combined with other identifiers or circumstances.
That means a healthcare practice should audit:
Public service pages
Condition-specific pages
Appointment pages
Contact forms
Provider pages
Patient portals
Scheduling systems
Thank-you pages
Campaign landing pages
Online intake forms
rather than assuming only the patient portal requires protection.
What Information Can Healthcare Tracking Technologies Collect?
The risk assessment should look beyond obvious patient names.
HHS identifies categories of information that can potentially be disclosed through tracking technologies, including:
- Medical record numbers
- Home or email addresses
- Appointment dates
- IP addresses
- Geographic location
- Device identifiers
- Unique identifying codes
- Information users type or select
- Other information associated with website activity
HHS also explains that tracking technologies can include cookies, pixels, web beacons, session replay, and fingerprinting scripts.
That makes patient data analytics much broader than the information appearing inside a CRM.
A healthcare analytics audit should therefore examine the entire technical path:
Patient → Browser → Website → Tracking Script → Tag Manager → Vendor → Analytics Platform → Advertising Platform
Every handoff deserves scrutiny.
GA4 Is Not the Only Healthcare Analytics Risk
Removing GA4 does not automatically solve the problem.
A practice can still have third-party tracking through:
- Meta Pixel
- Google Ads conversion tags
- Microsoft advertising tags
- LinkedIn Insight Tag
- TikTok Pixel
- Call-tracking platforms
- Heatmaps
- Session replay
- Chat widgets
- Embedded scheduling systems
- Social media scripts
- Third-party forms
This is why healthcare website tracking should be audited at the code level.
A practice that removes one analytics platform while leaving six advertising and behavioral scripts active has not necessarily solved the underlying data-flow problem.
The objective is not:
“Remove Google Analytics.”
The objective is:
“Understand exactly what patient-related information leaves our website, where it goes, why it goes there, and whether the disclosure is permitted.”
What a Healthcare Analytics Audit Should Examine
A proper HIPAA website compliance review should map every tracking technology installed on the website.
The audit should identify:
Tracking scripts
List every analytics, advertising, chat, session-recording, heatmap, and conversion script.
Data collection
Determine what each script can collect from the page, browser, URL, forms, clicks, and events.
Data transmission
Identify which external vendors receive the information.
Page-level exposure
Determine which scripts load on:
- Service pages
- Condition pages
- Appointment pages
- Forms
- Patient portals
- Scheduling pages
- Thank-you pages
Event configuration
Review event names, parameters, URLs, custom dimensions, user IDs, and other configuration settings.
Third-party integrations
Check whether the website passes information into advertising, CRM, call-tracking, or marketing automation systems.
Consent and disclosures
Review privacy notices, consent mechanisms, vendor agreements, and other applicable requirements with qualified privacy counsel.
This technical inventory gives the practice something more useful than a generic “HIPAA compliant” badge:
a documented map of its digital data flow.
What Should Healthcare Practices Do With GA4?
There is no universal answer that every healthcare practice can safely apply.
Google itself tells HIPAA-regulated entities to work with their legal teams to determine which pages are not HIPAA-covered and says authenticated pages are likely to be HIPAA-covered. Google also states that customers subject to HIPAA should not set Google Analytics tags on HIPAA Analytics.
That means the right approach is page-level and implementation-level assessment, not a blanket assumption.
A practice should review:
Which pages contain GA4?
What events are configured?
What parameters are sent?
Are URLs containing sensitive information being collected?
Are forms or user-entered information connected to analytics?
Are patient identifiers being used?
Are authenticated pages tagged?
Which third parties receive the data?
If your team cannot answer those questions, the HIPAA Analytics implementation deserves a technical audit.
A HIPAA-Conscious Analytics Strategy Does Not Mean Flying Blind
Healthcare practices still need performance data.
The solution is not to abandon measurement.
The solution is to separate business intelligence from unnecessary patient-level tracking.
Useful measurements can include:
- Organic search impressions
- Non-sensitive landing-page traffic
- Search visibility
- Keyword performance
- Google Search Console performance
- Local search visibility
- Aggregate conversion trends
- Technical SEO performance
- Page speed
- Indexation
- Content performance
- Appointment volume from appropriate systems
The specific HIPAA Analytics architecture should be evaluated by the practice’s privacy and compliance professionals.
The marketing team can then focus on the metrics that actually matter:
Which services are gaining visibility?
Which locations are attracting demand?
Which pages generate qualified inquiries?
Which search topics drive patient intent?
Which technical problems suppress organic visibility?
This is where healthcare SEO can operate without turning every patient interaction into an advertising data stream.
How RankMD Pro Approaches Healthcare SEO Without Treating Analytics as the Whole Strategy
RankMD Pro’s healthcare SEO framework focuses on patient acquisition rather than simply maximizing traffic volume. Its current service structure includes technical SEO, content and authority building, local search, AI search optimization, conversion optimization, and healthcare website development.
RankMD Pro’s Healthcare SEO Audit & Growth Strategy can identify technical SEO issues, search-performance gaps, competitive weaknesses, topical-authority opportunities, and conversion friction instead of relying solely on raw analytics volume.
For the technical side, RankMD Pro’s Technical SEO services focus on crawlability, indexing, medical schema, site architecture, performance, and technical foundations.
For practices building visibility around patient questions, RankMD Pro’s Content & Authority Building develops topical authority and medically focused content rather than producing disconnected keyword pages.
For local patient acquisition, RankMD Pro’s Local Search & Maps strategy targets geographic visibility, Google Business Profile optimization, local signals, and Map Pack opportunities.
For practices competing in AI-driven search, RankMD Pro’s AI Search & Answer Engine Optimization targets conversational intent, semantic entities, Google AI Overviews, ChatGPT, and other generative search environments.
If the website itself creates technical or conversion problems, RankMD Pro’s Healthcare Website Development focuses on healthcare-specific architecture, performance, usability, and conversion paths.
Practices can also explore RankMD Pro’s Mental Health SEO Services for specialty-specific search strategies or RankMD Pro’s Dental SEO Services when dental search visibility is the priority.
The key distinction is important:
HIPAA Analytics should measure the patient acquisition system not become a source of unnecessary patient-data exposure.
How HIPAA-Conscious SEO Can Still Support Google AI Overviews and ChatGPT
A privacy-conscious website does not need to disappear from search.
Google’s AI-search guidance continues to emphasize foundational SEO, crawlability, indexability, helpful content, and clear information architecture. The objective is to make content accessible and useful to search systems not to transmit patient information to HIPAA Analytics vendors.
For healthcare AI search, the priority should therefore be:
Strong technical SEO
→ Search-accessible content
→ Clear medical entities
→ Provider expertise
→ Local relevance
→ Original healthcare content
→ Internal linking
→ Structured information
→ Trust signals
→ Conversion-focused pages
This approach supports traditional search while also creating the foundation for visibility in AI-generated search experiences.
The HIPAA Analytics layer and the search-visibility layer do not have to depend on the same data architecture.
Why Healthcare SEO Audits Should Include Tracking Technology Audits
A conventional SEO audit may check:
- Title tags
- Meta descriptions
- Headings
- Internal links
- Broken links
- Schema
- Core Web Vitals
- Indexing
- Keywords
A healthcare-specific technical audit should go further.
It should also ask:
Which tracking technologies load on the page?
What information do they receive?
Where is that information sent?
Are sensitive pages being tracked?
Are forms connected to marketing platforms?
Are advertising pixels installed sitewide?
Are URL parameters exposing sensitive information?
Are third-party tools loading before consent where consent is required?
Does the implementation align with the practice’s privacy and compliance requirements?
This is why RankMD Pro’s healthcare SEO framework treats technical infrastructure, content, local search, AI visibility, and conversion as connected parts of a patient-acquisition system.
The SEO Data You Actually Need to Make Better Decisions
A practice doesn’t need every possible visitor-level signal to make smart SEO decisions.
You need answers to business questions.
Search demand
Which services and conditions are patients searching for?
Visibility
Which queries and locations are generating impressions?
Content gaps
Which patient questions aren’t being answered?
Competitive gaps
Which competitors own the searches your practice wants?
Local performance
Which locations and service areas are producing demand?
Conversion performance
Which pages and search themes contribute to qualified inquiries?
Technical performance
Which site problems prevent search engines from properly crawling, indexing, or understanding the website?
These measurements can support an effective medical SEO strategy without assuming that every marketing event needs to be tied to identifiable patient behavior.
7 Questions to Ask Before Installing Another Tracking Pixel
Before adding another marketing script, ask:
- What data does this tool collect?
Don’t stop at “anonymous analytics.”
Review the actual parameters and events.
- Where does the data go?
Identify every third-party recipient.
- Can the tool receive information from healthcare-related pages?
Review the exact URLs where the script loads.
- Can patient-entered information enter the event stream?
Forms, search boxes, URLs, and custom events deserve particular attention.
- Does the vendor provide the contractual protections your organization requires?
Do not assume a generic privacy policy is equivalent to a BAA or other required contractual arrangement.
- Is the tracking actually necessary?
If the business decision can be made without collecting the information, eliminating the collection may be the cleaner solution.
- Has qualified privacy counsel reviewed the implementation?
Technical teams can map data flows, but legal conclusions should come from qualified professionals.
What Google and HHS Actually Say About Healthcare Analytics
The safest strategy starts with the primary sources not marketing claims.
Google says healthcare organizations subject to HIPAA Analytics must not expose PHI to Google through Google Analytics and states that Google Analytics does not offer a BAA.
HHS explains that tracking technologies can create HIPAA obligations when regulated entities disclose PHI to third parties and specifically discusses technologies such as Google Analytics and Meta/Facebook Pixel.
HHS also makes clear that tracking technology itself is not automatically prohibited. The issue is how the HIPAA Rules apply to the information being collected and disclosed in the particular circumstances.
That distinction matters because the correct goal is not:
“Remove every script.”
It is:
“Build an analytics and marketing architecture that does not create unnecessary patient-data exposure.”
The HIPAA Analytics Trap Can Become an SEO Problem Too
A practice that panics and removes every measurement tool may lose the ability to identify:
- Declining organic traffic
- Ranking losses
- Technical errors
- Content gaps
- Local visibility problems
- Poor-performing service pages
- Conversion friction
The answer is not to choose between privacy and SEO.
The better approach is to build a measurement framework around aggregate search performance, technical data, content performance, and legitimate business outcomes, while carefully controlling sensitive information.
That is a much more sustainable approach to healthcare digital marketing.
A Better Healthcare Analytics Framework
A practical framework looks like this:
Step 1: Inventory
Find every analytics, advertising, tracking, chat, replay, and conversion script.
Step 2: Map
Document what each tool collects and where the information goes.
Step 3: Classify
Identify which pages and interactions could involve sensitive health information.
Step 4: Minimize
Remove unnecessary collection, events, parameters, and third-party scripts.
Step 5: Review
Have qualified privacy/compliance professionals assess the remaining configuration.
Step 6: Rebuild measurement
Prioritize aggregate SEO, search visibility, technical performance, content performance, and legitimate conversion reporting.
Step 7: Monitor
Re-audit the site whenever a new marketing platform, tag, form, scheduler, CRM, or analytics product is introduced.
This prevents the common cycle of:
Install → collect → discover risk → remove → lose reporting → reinstall.
FAQs About HIPAA Analytics, GA4 and Tracking Pixels
Is Google Analytics 4 HIPAA compliant?
Google does not represent Google Analytics as HIPAA Analytics and states that it does not offer Business Associate Agreements for Google Analytics. HIPAA-regulated entities must avoid exposing PHI to Google through Analytics.
Can healthcare websites use GA4?
The answer depends on the specific implementation, pages, data, and HIPAA obligations. Google specifically advises HIPAA-regulated entities not to use Google Analytics in ways that expose PHI and recommends working with legal counsel to determine which pages can appropriately use Analytics.
Is Meta Pixel HIPAA compliant?
A practice should not assume that Meta Pixel is appropriate for HIPAA Analytics healthcare activity simply because it is widely used in digital marketing. HHS specifically identifies Meta/Facebook Pixel among tracking technologies that can create privacy and security concerns for healthcare organizations.
Can a public healthcare webpage contain PHI?
Potentially, yes. HHS explains that information associated with visits to unauthenticated webpages can still involve PHI depending on the circumstances.
Should medical practices remove every tracking pixel?
Not necessarily. The appropriate approach is to identify what each technology collects, where it sends information, whether the activity creates HIPAA obligations, and whether the tool is necessary. A qualified privacy professional should make the legal determination.
What should replace risky healthcare analytics?
There is no single replacement for every practice. Options can include carefully designed first-party measurement, aggregate search reporting, technical SEO monitoring, Search Console data, server-side or privacy-conscious analytics architectures, and other tools evaluated for the practice’s specific compliance requirements.
Can HIPAA-conscious healthcare SEO still rank in Google?
Yes. HIPAA-conscious digital marketing does not mean abandoning SEO. Technical SEO, content quality, local relevance, site architecture, provider expertise, and other search fundamentals can continue to drive visibility without requiring unnecessary patient-level tracking.
Final Takeaway: Measure Your Marketing Without Turning Patients Into Tracking Profiles
The biggest mistake isn’t using analytics.
It’s using analytics without understanding the data flow.
GA4, Meta Pixel, advertising tags, session replay, and other tracking technologies can create useful marketing insights. But for healthcare organizations, the same technologies can create privacy and HIPAA concerns when sensitive information is disclosed to third parties.
HHS has specifically warned healthcare organizations about online tracking technologies, while Google states that HIPAA Analytics entities must not expose PHI through Google Analytics and that Google Analytics does not provide a BAA.
Your practice needs both:
Patient privacy + measurable search growth.
The answer is not more tracking.
The answer is better technical architecture, tighter data controls, stronger healthcare SEO, and measurement that answers business questions without unnecessary patient-data exposure.
If your medical practice needs to improve organic visibility while taking a more deliberate approach to healthcare website tracking, RankMD Pro can help assess your technical SEO, content, local visibility, AI-search presence, and conversion architecture.
Call RankMD Pro at (708) 497-9659 to discuss your healthcare SEO strategy.